If you’ve been holding off on AI features because of PII or compliance concerns, this one’s for you.
Until now, Holistics AI inherited the full permissions of whoever asked it a question - so if an admin or a Customer Success rep had PII access in the UI, AI got that same access the moment they used it. There was no way to hold AI to a stricter standard than the person asking.
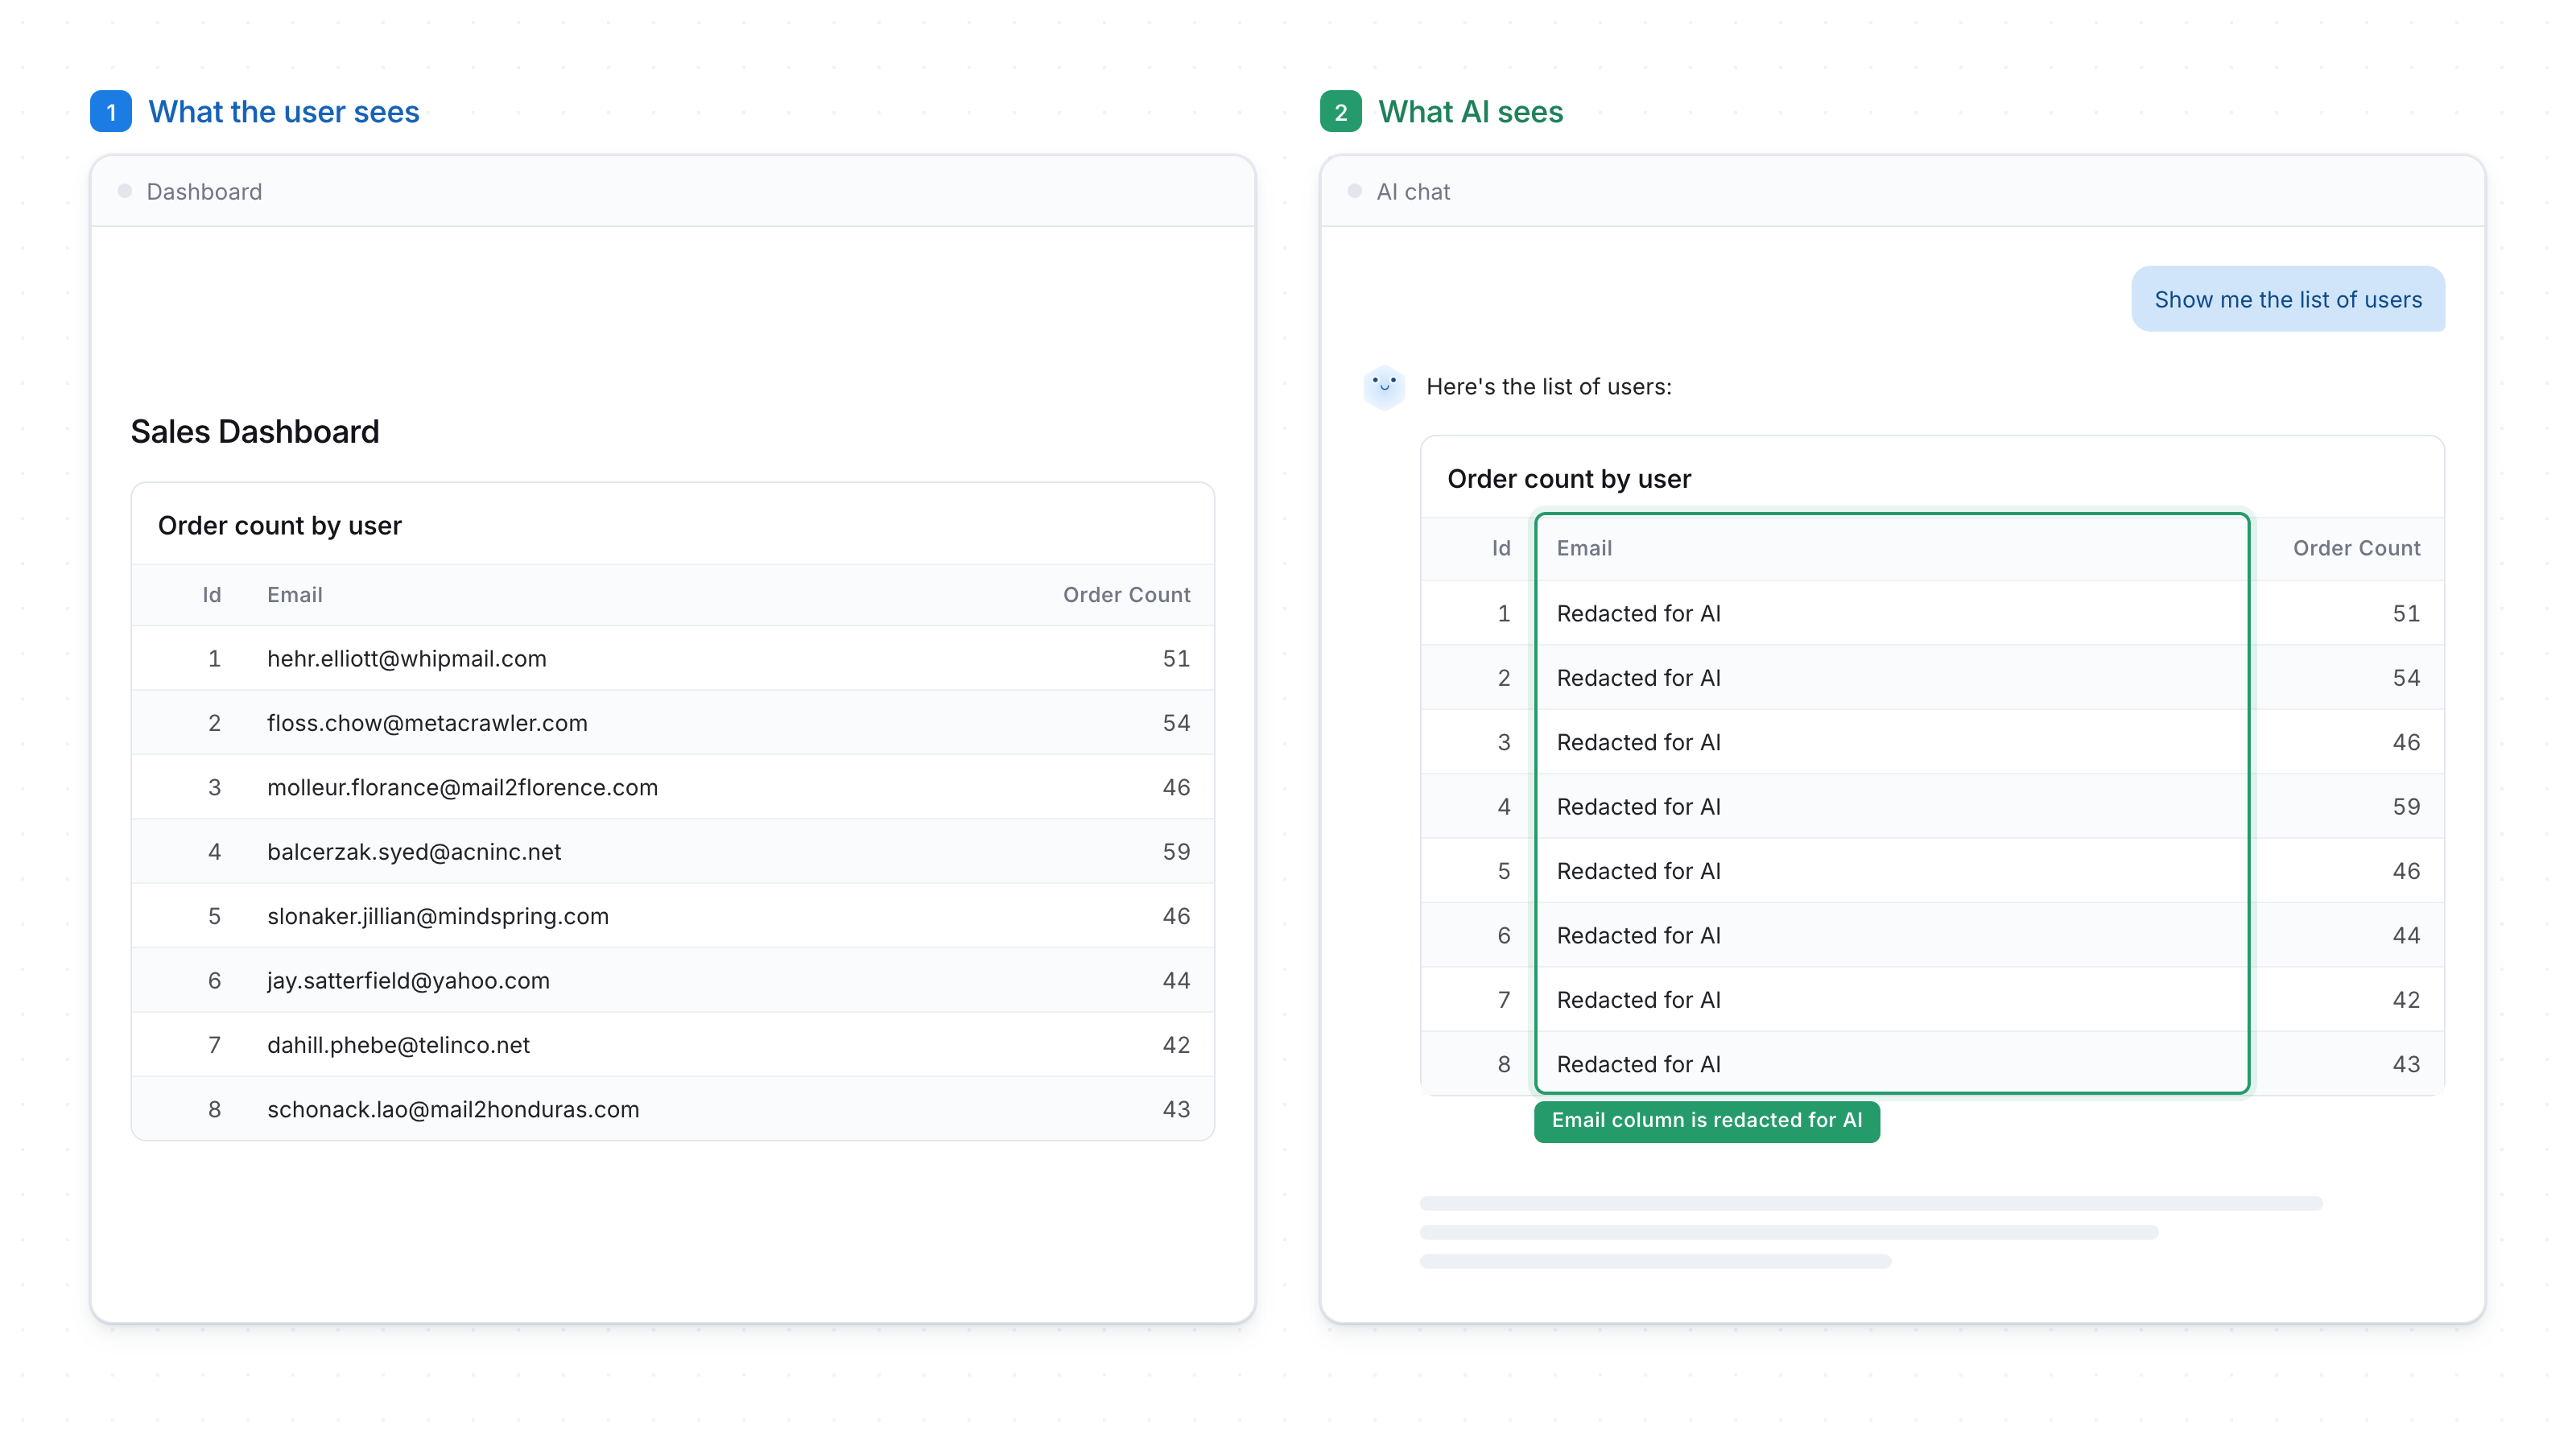
With the new AI user attribute, sensitive data can stay visible to the people who need it, while staying out of reach for AI - no matter who’s asking. Turn it on and you can:
- Mask specific columns (like emails) for AI only, via column-level permission
- Filter out entire rows for AI with row-level permission
- Route AI to a sanitized data source, or
- Add custom AI context to explain what’s redacted and why
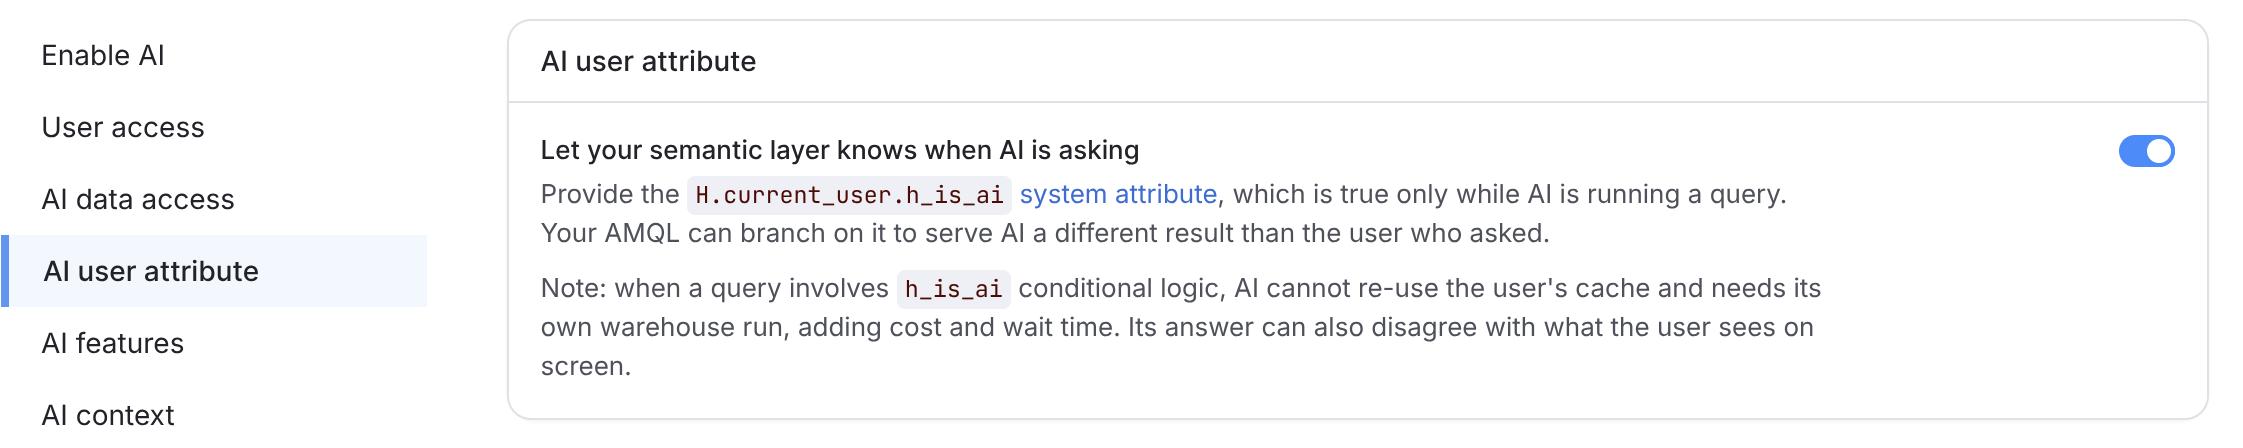
It’s off by default. Turn it on in Organization settings → AI settings → AI user attribute, then branch on H.current_user.h_is_ai wherever you’d normally use a custom user attribute.
Full docs here: Redact data for AI | Holistics Docs (4.0)
Let us know what you think! 